Guide
How to use AI with sensitive documents: a controlled workflow
Published
AT A GLANCE
Scope an AI document workflow around permitted data, verified provider settings, restricted access, source evidence and human decisions.
THE PROCESS AT A GLANCE
From document to decision
A simple review pattern to adapt to each workflow.
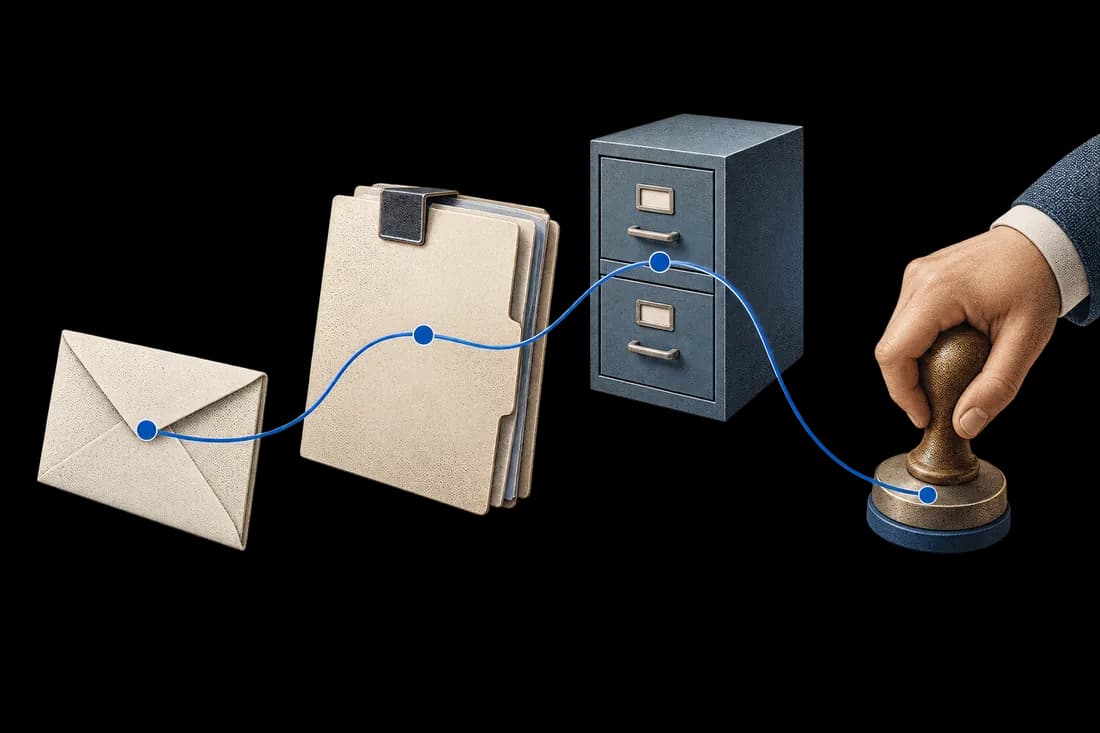
- SourceIdentify the document and source of truth.
- ExceptionShow what is missing or does not match.
- DecisionRoute the exception to the responsible person.
AI can help extract fields, classify files or prepare a summary from confidential documents, but the workflow must control who can access the information and what may leave the organization. Start with one permitted task and the minimum necessary data. Do not upload a whole archive just to discover whether a tool is useful.
Name the sensitivity and the intended task
Payroll, identity documents, bank details, medical records and commercial contracts create different risks. 'Sensitive' here means information requiring careful handling; it is not a claim that every example belongs to the same legal category. Have the responsible owner confirm the applicable obligations and authorized processing before real documents enter the pilot.
Fictional example: a finance team wants invoice number, date, currency and total from supplier invoices. For an initial technical test, use synthetic documents with those fields. Do not include employee identifiers or bank details unless they are necessary for an authorized step. A spreadsheet containing the extracted values needs protection too.
Choose the environment using verified facts
Compare an approved hosted service, a controlled private environment and local processing against your requirements. Ask where files and derived data are stored, which subprocessors are involved, who can access them, how long they are retained and whether inputs or outputs may be used for training. Check the exact service, contract and settings; a general provider slogan is insufficient.
Local processing can reduce external transfers, but administrators, logs, backups and connected tools can still expose information. A hosted API may offer controls appropriate to a particular workflow, but those controls need verification. Hosting location alone does not establish that the complete process is acceptable.
Protect the whole document path
Restrict intake, storage, review and export to the people and systems that need them. Use encrypted transport and storage, protect service credentials and separate customer or project access. Keep original documents, extracted text, summaries, search indexes and backups in the access and retention plan. Avoid copying confidential content into routine diagnostic logs.
If you mask data, verify the exported file rather than trusting black rectangles on screen. Text layers, metadata or hidden content may retain the original values. Replacing a name with a code is not necessarily anonymization when a mapping or other context still identifies the person. CNIL's design guidance explains why data selection and minimization belong at the start.
Treat document content as data, not instructions
A document can contain a sentence telling an AI to ignore instructions or send information elsewhere. OWASP describes this as indirect prompt injection. Keep the reader separate from action tools, restrict permissions and validate its output. A warning in the prompt alone is not a complete security boundary.
For the fictional invoice task, allow only the agreed output fields. Unexpected fields, missing values and contradictory amounts go to review. Show each proposed value with its page evidence. Do not let a document-reading model change supplier bank details, authorize a payment or send an external message on its own.
Test failure and deletion before expanding
Use synthetic or properly permitted examples to test cross-user access, incorrect extraction, hostile document text and interrupted transfers. Check that deletion covers the intended files and derived copies according to the retention plan. Record an owner for incident response and a way to suspend processing. The pilot passes when its controls and recovery work, not merely when a summary looks convincing.
Sources and further reading
CNIL: privacy in AI system design
OWASP: prompt injection prevention
NIST: Generative AI Risk Management Profile
Apply this to your workflow
To scope a document workflow, prepare a permitted example, the required fields, your current system and the person who reviews exceptions. Begin with synthetic examples when confidential data is unnecessary.